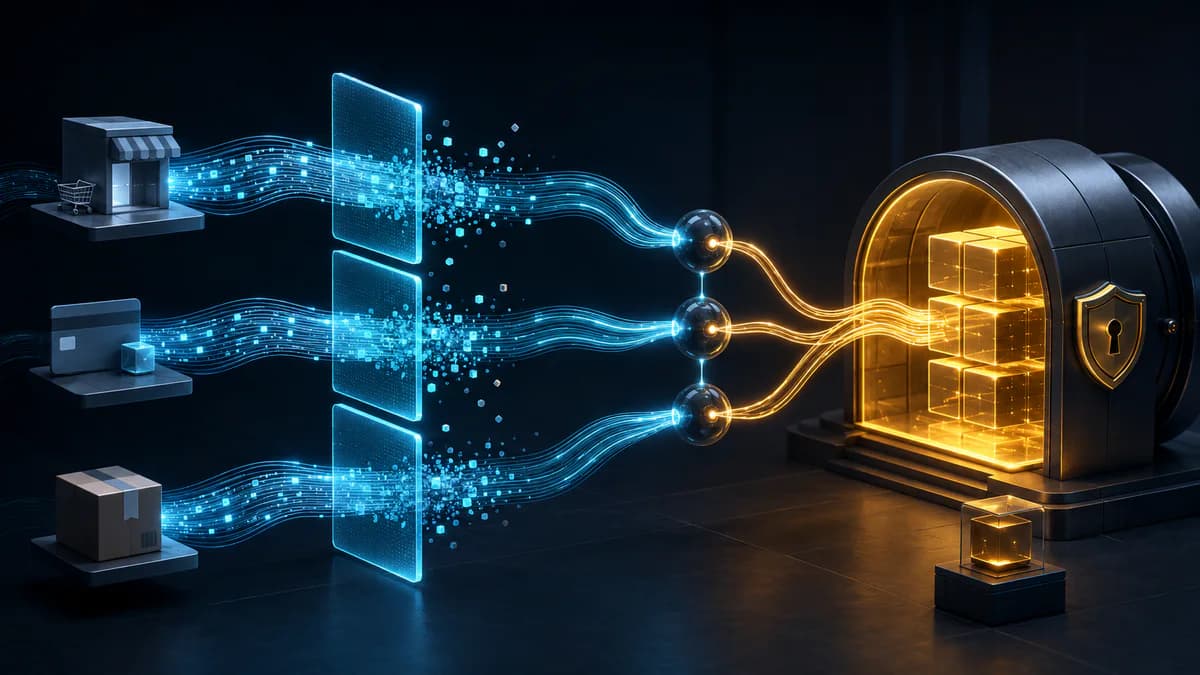
Ecommerce logs must help teams reconstruct a checkout failure, an unusual refund or privileged access without becoming a hidden copy of customer data. The risk grows when every service records complete payloads for convenience: an observability pipeline can end up holding tokens, session identifiers, addresses, payment data or secrets under unclear access and retention rules. The answer is not to stop logging. It is to define a contract that states which events are necessary, which fields are allowed and where each protection is enforced.
Separate operational, security and audit purposes
The first design decision is purpose. Operational logs explain service health, latency and failures. Security logs reveal failed authentication or authorization, privileged actions and suspicious behaviour. Audit records reconstruct material actions such as order changes, refunds, exports and configuration changes. These needs may share transport and storage components, but they should not automatically inherit the same fields, audiences or retention periods.
A useful event describes a decision instead of copying a request. A refund record needs the technical actor, a pseudonymous order reference, the action, result and reason. It does not need the complete customer payload. Clear purpose reduces noise and makes it possible to justify every retained field.
Define a minimal structured schema
A consistent schema answers when, where, who and what. It includes timestamp, service and version, action, pseudonymous reference, outcome, reason or severity and a correlation ID. The reference should support an authorised investigation without directly exposing an email address, name or public order number. Input from browsers, webhooks, files and partners remains untrusted even when it is written into an apparently harmless logging field.
Correlate the journey without copying payloads
The frontend, API, payment layer and OMS can propagate separate but linkable technical identifiers: request ID, trace ID, correlation ID and a pseudonymous transaction reference. An incident can then cross service boundaries without replicating a cart, address or provider response. Identifiers need controlled format and length and must never become containers for business data.
Apply allowlists and minimisation at the source
An allowlist is more reliable than an expanding list of forbidden words. Each event type declares permitted fields and discards everything else. Passwords, tokens, keys, connection strings and card or bank data must not enter the log. Session identifiers and PII should be excluded or, where a documented need exists, masked, encrypted or transformed. Hashing does not automatically provide anonymity: values drawn from small or predictable spaces can still be recognised by comparison.
Choose the transformation for the use case
Removal is best when the value has no operational purpose. Truncation keeps a non-sensitive fragment; masking limits display; pseudonymisation supports controlled linkage; encryption retains recoverability for authorised roles. The choice must be tested with real message shapes, including error messages, stack traces, headers and attributes automatically attached by libraries.
Build layered controls into the pipeline
The application handler enforces the event schema and blocks forbidden fields. A collector can remove, hash, truncate, filter or transform attributes before export. The ingestion layer adds a final detection and masking policy. A managed capability such as AWS log data protection is an example of that final layer, not a substitute for source minimisation. Ingestion masking does not retroactively repair data already stored, and permission to reveal a value must be restricted, audited and reviewed.
Prevent log injection and ambiguous records
External CR, LF, delimiter and control sequences can forge lines or fields. Code should sanitise separators, impose length limits and encode output for the selected format. Viewers must also treat log content as data rather than markup or commands. A structured format helps, but it does not remove the need to validate untrusted values.
Protect access, transport and integrity
Logs travel through networks, collectors, queues, storage, backups and analyst extracts, so protection must cover the full route. Encryption in transit and at rest, least privilege and separated roles reduce exposure. Access, sensitive searches and unmask operations need their own audit trail. Detecting modification or deletion requires integrity controls, central copies and, where appropriate, append-only or read-only destinations for analysts.
The same administrator should not be able to produce, alter and erase evidence without a trace. Separation does not remove risk, but it makes actions attributable and supports periodic permission reviews.
Critical audit events need an authoritative copy and separate alerts for delayed delivery, expected drops and unexpected loss. Temporary permissions should expire automatically; exports must be labelled and their recipients recorded, protecting the analysis path through to the local file.
Design retention and deletion around purpose
There is no universal duration for every log. Retention follows operational purpose, legal duties, contracts, risk and investigative needs. Temporary debug data, security events and audit evidence may use different lifecycles. The policy must include primary storage, backups, exports, test environments and files downloaded by analysts; otherwise a nominal deletion leaves forgotten copies behind.
Each event class needs an owner, expiry rule, approved exceptions and evidence that deletion ran. Longer retention should be an explicit decision rather than the accidental result of storage without a lifecycle.
An inventory for each sink maps producers, readers and derived copies. Teams verify lifecycle execution with deletion evidence and backup restore tests so expired records do not return. Any change to a retention period triggers a fresh review of purpose and legal basis.
Test failures and measure the control
The pipeline must be exercised with full disks, lost connectivity, denied permissions and resource exhaustion. Checkout should not collapse because a logger is slow, but it should not spill sensitive values into an emergency console either. Buffers, backpressure, drop policies and fallbacks need documented behaviour and observable health. Tests should include CR/LF input, synthetic tokens, oversized payloads and unauthorised access attempts.
Useful measures include schema coverage, sensitive-data findings, pipeline and drop health, volume by event type, retention and deletion execution, access and unmask audits. A release gate checks that new events follow their allowlist and that dashboards and runbooks have owners. To build useful ecommerce logging without unnecessarily expanding exposure, explore our services for ecommerce systems or discuss the design with our team. Success means a trace that is correlatable, protected and deletable, not the largest possible number of log lines.
Frequently asked questions
Which data should never appear in ecommerce logs?
Passwords, tokens, keys, connection strings and card or bank data should be excluded. Session IDs and PII should be removed or transformed only for a documented need.
Is masking at ingestion sufficient?
No. Use source minimisation, collector transformations and an ingestion control. Masking also does not automatically repair sensitive data already stored.
How can services be correlated without logging the customer?
Propagate request IDs, trace IDs, correlation IDs and controlled pseudonymous references without including email addresses, postal addresses or payment payloads.
How long should logs be retained?
There is no universal duration. Purpose, law, contract and risk drive the policy, which must also cover debug data, backups, extracts and deletion evidence.
Related articles
Ecommerce distributed tracing: diagnose checkout and orders with OpenTelemetry
An operational method for tracing checkout and orders, propagating context, correlating providers, protecting data and sampling without losing incidents.
Ecommerce secrets management: rotate credentials without downtime
An operational method to inventory, distribute and rotate checkout API keys and credentials without embedding them in code or interrupting orders and integrations.
Reducing ecommerce PCI DSS scope with hosted fields and tokenization
A provider-neutral implementation guide to keeping PAN and authentication data out of merchant systems while retaining server controls, ownership and audit-ready evidence.